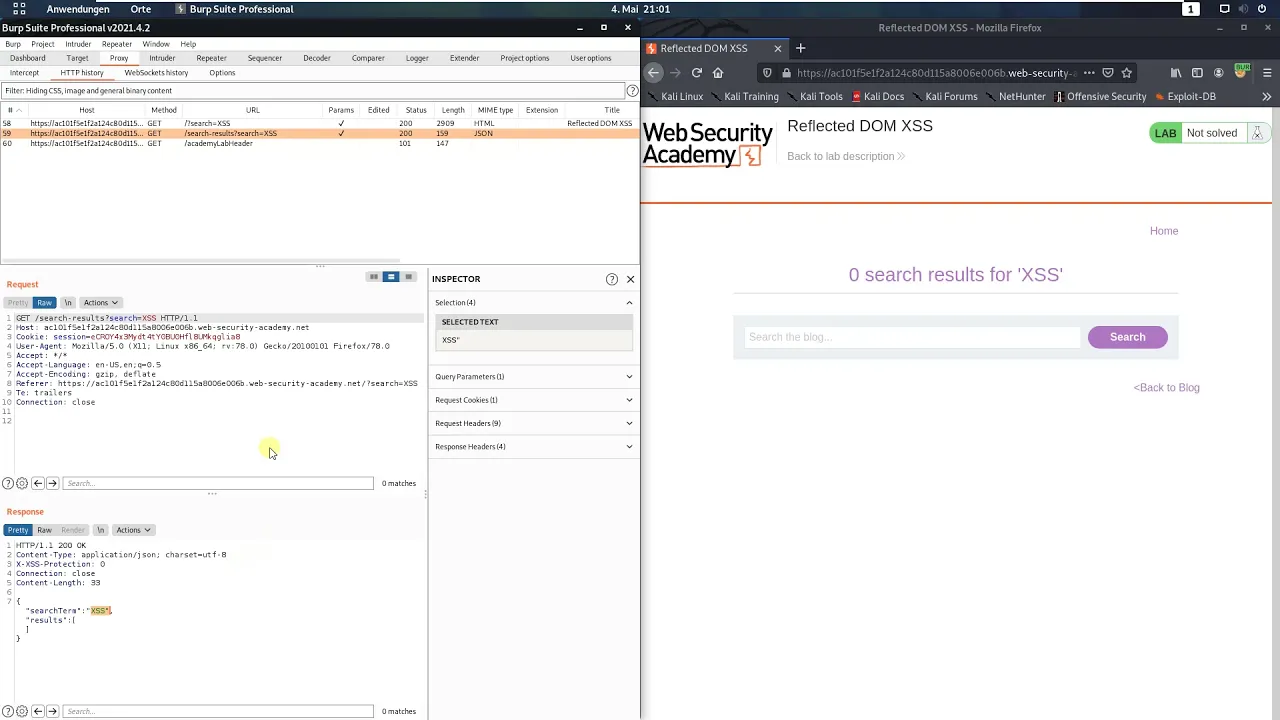
hi guys we will solve the lab reflected dom xss the level of this lab is practitioner and the goal is to create an injection that calls the alert function let us access the lab make sure that you're proxying your traffic through burp and in burp deactivate the interceptors on button go back to your browser and put in the following string in your search field and click the search button now open in burp proxy the http history and you'll see there's a get request to the endpoint slash search minus recites question mark search equal xss open
it and you see in the response section the search is in a json format okay now go to the target tab and you see there's our lab host and there's also a directory named resources and inside resources is a directory named js and if you open this directory you see a js file named search results but we can't um see any response for this file for that go back to your browser and click the refresh button and you see now we get the res the response for that file with the file content and within this
javascript file look for the evil function and you see that our search is within an the function okay now you can experiment to find out which characters are blocked or escaped by the application but to solve the lab you need backslash double quotes minus alert one and slash send this search to the application [Music] you see we call it the javascript function alert and we also solve the lab