It's time for security Now Steve Gibson is here his reaction to Microsoft's announcement you'll have to have TPM 2.0 for Windows 11 yeah you might imagine Steve's a little upset he'll talk about that in just a little bit uh Apple patents AI recognizing people by the clothes they wear uh the FTC is going after data Brokers and Steve's going to take a look at coding with chat GPT he has some very Interesting thoughts it's all coming up next on security Now podcasts you love from people you trust this is Twi this is security Now with
Steve Gibson episode 104 recorded December 10th 2024 a chat with GPT it's time for security Now the show we cover your security online your privacy your safety what's going on in the world of cyber security With A Man A Plan Panama no no I'm sorry that's that's wrong Mr Steve Gibson that's who I'm talking about of of GRC Fame hi Steve hello Leo great to be with you for uh what is this episode 1 like I don't know episode 104 for de it says it right at the top of the show notes big letter hey
and what happens on the holidays cuz we have some I think things collide with Tuesdays um I don't know if oh uh we are doing a best of for you right Anthony I Think we are uh so there'll be a best of security now in fact people can contribute their thoughts uh so they'll be a best of and then we're off for a week right or does the best of fill in for like the between Christmas and Christmas is Wednesday so Christmas Eve yeah probably when the best of is Anthony are we planning to do
a New Year's Eve show or not no one knows I will have to ask the boss can you hear me yeah we're dark uh New Year's Eve yeah so uh no show on New Year's Eve Steve no oh sorry I didn't you used to say no no no I got to do a show you don't care as much okay there's that wife again you have a you have a life now you're going to be dancing I will be kept busy with endless social what are we doing now honey before you had a wife going over
you danced with the James tiberious Kirk on our on our set much more Nimble back then my friend that would I'll never forget that we did Our 24-hour New Year's Marathon Steve came up for it one year and danced with a card cardboard cutout of of the captain yeah I don't remember I remember I was either completely sober or I was way far from it I think actually I was completely sober people would have thought that I was inebriated you were in the spirit fool of myself but no of course on the other hand you
were getting your butt tattooed so it was quite the event that year so that all uh By the way video of that exists and is still available so don't don't don't go no don't uh I think it's on our YouTube channel all right what are we talking about uh more seriously on a more serious note what are we talking uh uh today's podcast is titled a chat with GPT and I listened to the end of Mac break weekly where Andy and and Alex was singing the Praises Cody Alex has had The experience and it's interesting
because he characterized it much as I have that that is he he was going further because he was wanting it to basically create an entire application framework with most of the things filled in except for a few things that you know it just couldn't get right um ah anyway I had an experience over the weekend that you know again it was like okay what what H what and so I'm gonna share that and it Is the I have to take us a little bit into the weeds of the questions that I was asking in order
to set up the dialogue that we had and then I have an announcement to make uh but so so this again today's episode titled a chat with GPT but we have a lot of stuff to talk about all telom providers have been hacked and may still not be safe to use also which I heard you mentioned on Mac break so now the government is recommending that we use our own Encrypted Communications uhhuh uhhuh okay also the plan to obsolete all non TPM 2.0 PCS remains well underway Microsoft must be feeling the heat so they're T
they're taking the time not to apologize uh also whoops Microsoft's product activation system has been completely hacked like fully the things that that the hackers weren't previously able to activate they can Now activate so all windows and Office Products may now be easily activated without any Licensing also we're going to talk about the coming AI patents Apple patented AI recognizing people by what they're wearing after seeing video of their faces and noting what they were wearing so well that's an invention okay yeah uh Zoom wasn't encrypting their early video conferencing and they're still trying to
get out from under the mess that those lies that they told back then created for them AWS introduces physical data terminal Locations that of at a metropolitan area near you where users will be able to go to perform massive data transfers to and from the cloud bring your own hard drive just bring exactly also the FTC fortunately has set their sites on data Brokers so we can hope that something comes of it uh grc's email finally gets beamy and I had a lot of feedback from our listeners who received email from me showing our Ruby
G for the first time so I'll I'll update us on that we also have a bunch of terrific listener feedback uh one I'm going to go into some depth about authenticator policy in use uh also uh a a a new and free point-to-point link Service uh tours snowflake proxy uh also a bunch of feedback from our listeners suggesting solutions for linking PCS and smartphones which I complaining about my lack of ability to do uh also one Listener said Steve H how do I refill my soda stream canisters again so I'll touch on that briefly and
then we're going to talk about the the like shocking well to me because you know I was born in the mid-50s conversation I had with chat GPT uh over some subtlety of assembly Lang language syntax and how that went so and of course we've got a great picture of the week for our listeners so I think a podcast that'll keep everybody Entertained I'm very curious about chat gbt's Assembly Language capabilities that will be that will be interesting you know a lot of uh it's actually a lot of controversy this year because people are using llms
to solve the Advent of code problems in seconds it's immediately obvious because it's I mean even somebody who's professional coder you know competitive coder will take a few minutes at least uh because you got to look at the problem read it Solve it write the code these guys are doing it four or five seconds it's obviously wow they're using an L wow well and it's sad too right I mean like the point if you enjoy playing chess then why use a computer to cheat for you but people do that even at the highest level and
I know it's very bizarre I don't get it you know it's so it's like me I don't want it to program I love to code the reason Leo when I had 32 employee oh no 23 sorry I got the digits Backwards I had 23 employees I was upset because they were getting to have all the fun I had meetings and I didn't want to have meeting that's no fun I wanted to do the R&D and write the code and worry about you know design ads and all that and so now it's just me do it
all with GRE and Sue to do this stuff yeah you don't want to do the bookkeeping or support that part they can have yeah that they are my chat gpts in that case but you know it's probably only a matter Of time before you've got an AI to do some of that stuff too yeah anyway we'll talk about that I'll be very curious what you found so that's going to be fun but that's just around the corner because we're going to have a word from our fine sponsor right now the folks at Lookout today every
company is in the business of managing data right that's you know that's your lifeblood it also means that every company is at increased risk of data exposure and loss if you Listen to this show you know you see the headlin Cyber threats breaches leaks and one thing has become apparent cyber criminals are getting more sophisticated every single day modern breaches now happen in minutes and not months so at a time when the majority of sensitive corporate data has moved to the cloud those boundaries the traditional boundaries between the outside world and the inside world have
just have dissolved and the strategies for Securing that data have just fundamentally changed that's why you need Lookout from the first fishing text to the final data grab Lookout stops modern breaches as swiftly as they unfold and that's wherever your data is on a device in the cloud across networks even if it's sitting on a laptop at a local coffee shop where your employees are working remotely Lookout gives you clear visibility into all your data at rest and in motion you'll monitor you'll Assess you'll protect without sacrificing productivity for security I mean you got to
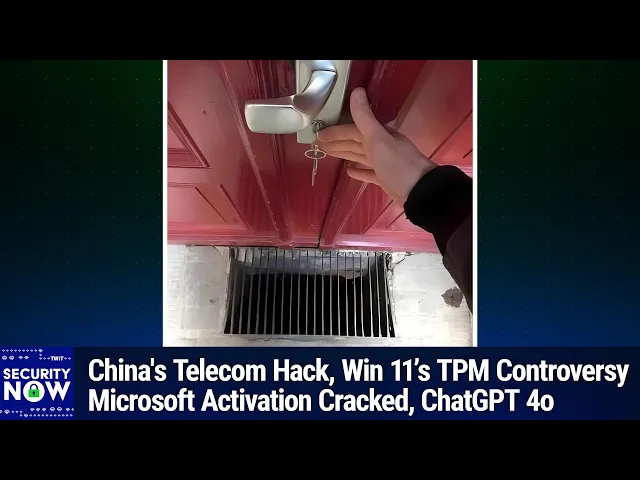
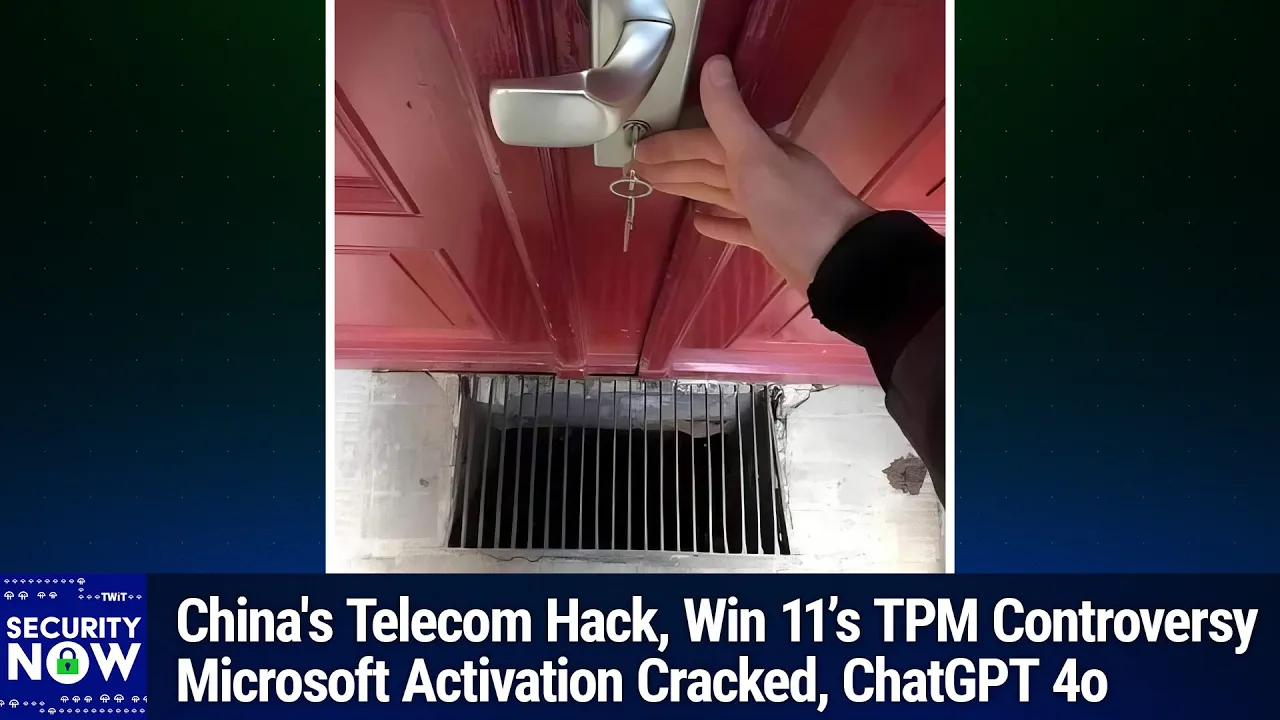
have that latte with a single UniFi Cloud platform Lookout simplifies and strengthens they've reimagined security for the world that will be today right plan ahead visit lookout.com to learn how to safeguard data how to secure pure hybrid work and yes it's a single platform reduce it complexity that's lookout.com L Kut lookout.com lookout for Lookout we thank Him so much for supporting security now and the good work that Stephen Gibson is doing I am ready Mr G I haven't looked so this picture was a no-brainer to caption it was demanding the caption what could possibly go
wrong all right I'm scrolling up now to see it for the first time oh oh boy that is a terrifying site so okay now okay I'm going to I'm going to share the feedback that we've already Received from one of our listeners yeah who asked chat GPT what this pict picture what was the significance of this photo that's interesting so and again Leo it's and this this is I I okay so he wrote I of course also being blind have t have taken to chat GPT to get even better descriptions of images I look forward
to the upcoming show to see how it did but I think you'd have to agree that the bar for image descriptions is now insanely High it's certainly much better than anything we've had up until now including Microsoft's and Apple's own Vision models useful as they've been in the past and being offline here's what I asked and the response so our blind listener who received the email there was 13,670 emails went out last afternoon to our to our listeners he wrote can you describe this in detail and then he gave it the URL uh grc.com sn14
jpg you know jpeg image CH from that URL this technology we have today said the image shows a humorous but precarious scenario oh a red door with a silver handle is being unlocked using a key the person holding the key is positioned above a metal grate that covers an open pit or vent below the door the text above the image reads this photo demands the caption what could possibly go wrong the concern writes Chat GPT is obvious if the key slips or Falls it would likely drop through the gaps in the GD theit below making
retrieval very difficult the situation highlights a classic Murphy's Law setup where the most inconvenient outcome seemes seems inevitable holy cow that is really good like what have what what um I can only think that maybe before we get too excited that that Image has showed up somewhere uh in a newspaper with similar dialogue below it and that chat gpt's making the connection but that's pretty impressive you know I my blog is uh hosted by a a site called micro.pig if you have images put an ALT tag for unsighted uh readers like yeah your correspondent there
and ites does a very good job I used to write my own alt tags and I have to say this is a lot easier to let the AI do it but that is Above and beyond that's so I don't know that I need to further describe the picture because CH P just did it's and and one one person commented that it might be a grate which is used in snowy country to allow people to to scrape the the the snow the pack snow off the bottom of their shoes although then I would think the great
would the the the bars would be moving would be oriented horizontally to make it more easy to scrape I just think it was an Inconvenient location for a drain to be you know I mean as we've seen there are many instances where you wonder okay who's in charge here this doesn't make any sense but anyway it was a perfect setup for uh the topic we're going to get to at the end of the day so uh wow and uh I I shared our our note with are also um uh unsighted listener last week who thanked
me for always going to links to describe the photos which she gets so much uh enjoyment from so I just wanted To give her the tip that uh Chad G BT is standing by uh and frankly Leo I'm gonna it'll be interesting to to feed it maybe some more obscure images that that seem less likely to have been you know populated on the internet than just see if this was an anomaly or again it's just we have there there's something going on and uh uh I don't want to step on my plan but uh we'll
get there by the end of the podcast I have some some news um okay So salt typhoon is the name that's been given to this group for the past several months there have been various news reports of Chinese state sponsored attacks against this or that us telecommunications company I I've seen them I haven't mentioned them on the podcast because we've had so much else to talk about and I don't know it sort of didn't seem to have reached critical mass but that changed last week an newberger the US Deputy National Security adviser said that at
least eight us Telos and actually apparently a total of 80 overall but eight us Telos have been hacked and the US is now getting set to take some coordinated definitive action so I think we need to do a bit of catching up on the podcast the best reporting I found on this was headlined Chinese hack of global tcom providers is ongoing officials warn um with the subhead officials from the FBI and sisa say the major Chinese hack Began late spring and they strong strongly the strongly urging Americans to use encrypted Communications like what okay okay
so the reporting says last Tuesday Federal officials said that the federal government began investigating a major Chinese breach of global telecommunication systems last spring and they further warned that the intrusion remains intrusions remain ongoing and that it's Likely larger in scale than previously understood the hack was first announced publicly in October and has been attributed by US Agencies to a Chinese government linked hacking group known as salt typhoon the effort targeted dozens of telom companies in the US and globally to gain access to us political leaders and National Security data neither the timeline of the
hacking effort nor the scope of the intrusion were previously closed Jeff Green Executive assistant director of cyber security at cisa and a senior FBI official said Tuesday that while agencies started cooperating on their investigations of salt typhoons activities in early October the effort was first detected in late spring and early summer he also warned that the breach is ongoing and that there was much law enforcement still did not know Green said quote we cannot say with certainty that the aders AR has been Evicted wow we're on top of tracking them down but we cannot with
confidence say that we know everything nor would our partners green strongly urged Americans to quote use your encrypted Communications where you have it unquote adding that quote we definitely need to do that kind of look at what it means longterm how we secure our networks wow yikes that's definitive and notice the irony of the government telling its citizens that they need to use their own Encrypted Communications apps wherever possible because the networks of the Telecommunications providers are well turn out to be insecure and there doesn't appear to be a lot that could be done about
that and we're not even sure we got rid of them or what they're doing or what's going on they're cockroaches we can't get rid of them they're in there permanently it's course ironic right because our governments have been chafing over their citizens use of the Same encrypted applications with the government is unable to to penetrate there's even more irony because the salt typhoon people are taking advantage of wire Taps that were inserted by Kalia 20 years ago because law enforcement said they needed them the irony is endless yep so maybe at as many as 80
you know 8 Z telecommunications companies and internet service providers including AT&T Verizon and T-Mobile are believed to have been infiltrated in the hack There are 80 of them in the 80 globally yeah basically all of them right because we we don't want to miss anybody with our Kalo warrant T-Mobile was the most recent one in the news anyway earlier last Tuesday sisa the FBI the NSA and partner agencies in New Zealand Australia and Canada released a joint Alert warning that Chinese hackers were targeting major global telecommunications providers officials declined to comment On specifics but acknowledged
that quote there were servers used in various countries to facilitate this activity by the Chinese unquote interestingly the UK K did not sign on to the alert making it the only one of the five I's intelligent sharing Group which was omitted green attributed this to each country having different considerations and timelines unquote okay a spokesperson for the UK's National cyber security Center said Tuesday that the agency supports our International Partners issuing this advisory to help improve the collective resilience of telecommunications infrastructure but at the same time didn't sign on to it but oh yes we're
supportive we're just not going to put our name on it um and he also said the UK has a separate approach to mitigating cyber risks to its telom providers okay anyway the officials from the FBI and sisa noted in their briefing that there were three groups of victims Targeted in the hacks the first group was an undisclosed number of victims mostly in the United States capital region you know meaning DC yeah according to the officials who were impacted by stolen call records from telom companies the second group were a small number of political or government
linked individuals all of whom have been notified by officials So based on the records of this intrusion they at least were able to identify the targets of These attacks who had their private Communications compromised according to to a senior FBI official who spoke anonymously as a condition of briefing the reporters while the officials did not specify exactly how many officials were targeted it was previously reported that the phones of president-elect Donald Trump and vice president elect JD Vance were among those compromised in both cases prior to the US national election in many cases the voice
and Textual content of call connections and conversation were obtained by Chinese attackers in other words not just metadata interesting well it's a wiretap so yes it was wiretap in addition the Chinese hackers also accessed and copied us court orders which the FBI officials said were attained through the as you noted Leo Communications assistance for law enforcement CA Clea statute program this program allows law enforcement and Intelligence agencies to submit court orders around intelligence collection from telom providers when pressed on whether hackers were able to assess court orders for intelligence collected under the foreign intelligence surveillance
act fisa which allows us intelligence agencies to collect data on foreign targets the FBI official declined to answer directly but acknowledge that the Kalia environment does include court orders for f Investigations the major hacking campaign has been an issue of increased concern for us lawmakers in recent weeks the Senate intelligence committee chair Mark Warner describing it as quote the most serious breach in our history now again we installed the Taps so gee oops I mean th this is the like isn't this the perfect analogy for why we don't want the government to have access to
encrypted communication this is the whole they're not good enough at it no One is any back door will eventually be discovered yep Senator Mike rounds ranking member of the Senate armed services committee uh cyber subcommittee said during a panel at last month's Halifax International Security Forum quote unless you are using a specialized app meaning you know our own encryption any one of us and every one of us today is subject to the review you by the Chinese communist government of any cell phone conversation you have with anyone In America okay this is Senator Mike grounds
at you know the with the Senate armed services committee cyber subcommittee saying unless you use something else that is just don't talk on the phone you know do something else unbelievable anyway I think this news highlights the clear need for in independent third-party endtoend encrypted video Voice and text messaging systems we being told that the conversational content not just Connection metadata of anything carried by our International and National telecommunications carriers can no longer be considered to be secure from eavesdropping by advanced persistent threat actors who want to know what's being said well they can have
my phone calls I I'm not saying anything right but you know there are there are conversations which we don't want China to have so if nothing else this news which has now Been officially recognized weakens any argument against allowing users of public telecommunication systems from providing and using their own truly secure endtoend encryption for their conversations and cont content you know the analogy is to the internet right the internet is a similar public network which is not itself secure so to it we've added a layer of authenticated TLS encryption to enable point-to-point endtoend Communications security
https and no one has any problem with that so what's the difference and what's the big deal I should point out uh a uh reporter at Forbes looking at the actual request by the FBI that people start using encryption the request said use responsibly managed encryption which is encryption that allows us to subpoena the clear text because we have responsibly managed Telcom and how's that working out so what they're saying Is use encryption but uh uh not too good so what we should all use signal or whatever it is that you threa whatever it is
that you like what do you what would you use these days because you need to make phone calls it has have audio as well right yeah I guess I would use signal if I had if I had to have a a an endtoend encrypted uh system that I trust uh WhatsApp is using the signal protocol so it's it it's the same as signal if you Trust meta I mean I'm sure iul trust meta but okay yeah um wow yeah I I mean certainly signal doesn't have can't have any other agenda because their entire you know
business model is is they don't even have a business model right I mean what is their business there is no business model it's just yeah what a world huh yeah it's just you got to do what you suggested go out and field take off all your clothes go out in the field far Away from any a comforter with with someone you you know and if you want to say private bring them naked with yeah bring a space heater a little portable you know yeah make sure it's not made in China though that's oh yeah you
don't want an interconnected Internet connected space heater no no it is it is it is it is the world we live in at least there is no privacy no no that's a sad fact okay so TPM 2.0 and we're not kidding oh we talked About this with Paul and Richard last week wow yeah a posting to the windows IP Pro blog last week was titled TPM 2.0 a necessity for a secure and futureproof windows 11 and of course I titled this bit of news TPO 2.0 and we're not kidding um I'll give everyone a sense
for this by sharing just the first few paragraphs of what is a quite lengthy posting by Steve hosing whose info on X identifying identifies him as senior program manager for Windows Commercial and I I I'm you know because I try to get my spelling correct I noted that he has commercial spelled with 1 M so I don't okay anyway he wrote with Windows 10 end of support approaching this is right next October it's important to revisit a key minimum system requirement for Windows 11 trusted platform module TPM 2.0 let's discuss the role of TPM and
its value for those of you who have made the transition to Windows 11 you'll also Learn how to check your TPM status and how to prepare for Windows 11 presumably for those who haven't yet transitioned TPM refers to a dedicated chip or firmware that offers Hardware level security services for your device it securely houses encryption Keys certificates passwords and sensitive data shielding them from unauthorized access additionally TPM is tasked with cryptographic operations such as producing random numbers encrypting and Decrypting data and confirming digital signatures TPMS are available from many different manufacturers including Microsoft on supported
CPUs with pluton and I'll just note all of that's true of TPM 1.2 equally okay but there there's differences we'll get to that in a second he continues you know that Windows 10 is approaching end of support in Windows 11 TPM 2.0 Advanced encryption techniques offer more Versatile and critical Key Management for contemporary it infrastructures as compared to its predecessor TPM 1.2 integrating with features like secure Boot and windows hello for business TPM 2.0 enhances security by ensuring that only verified software is executed and protected confidential details it's true that its implementation might require a
change for your organiz ization yet it represents an important step toward more Effectively countering today's intricate security challenges and finally I'll finish with him saying the TPM 2.0 helps keep your identities more secure and your data protection more robust can you ensure operating system Integrity upon startup yes can you better protect sensitive information data and secrets yes it provides a vastly more more efficient and secure platform for Windows 11 vastly okay to use through advanced Encryption methods improved industry standard cryptography increased isolation and greater interoperability with other security functions okay enough of that and that's
just like the tip of his Iceberg uh okay so is TPM 2.0 really better than 1.2 yes yes it is without a doubt it offers newer updated cryptographic operations such as elliptic curve crypto and sha 256bit sha2 error hashing and Message authentication functions instead of just sha1 and it provides a privilege management hierarchy rather than just the single level hierarchy which isn't really a hierarchy the single level offered by TPM 1.2 but here's the problem while 2.0 is without a doubt new and improved and should be adopted and used going forward there's never actually been
anything found wanting about TPM 1.2 that might Force its abandonment as we've observed from the beginning this isn't this is an arbitrary requirement TPM 1.2 had been working just just fine for everyone and still is until Windows 11 came along I would have no problem with Windows 11 taking advantage of the more secure features available from 2.0 if and when they were available in the underlying platform but it should be up to Windows users whether or not they feel they need to upgrade their PC Hardware to obtain that additional security under Windows 11 and and
Stephen wrote it's true that its implementation might require a change for your organization right a change what he meant is that the move to Windows 11 May forcibly obsolete all of an organization's current stock of PCS which are otherwise right now still quite happily running Windows 10 but none of those machines will run Windows 11 and Microsoft's continuous IV Drip of life support to continuously repair the Apparently endless supply of serious security bugs in Windows 10 will be coming to an end next October as we covered previously last Halloween Enterprises and individuals will have the
option of paying for extended life support for up to three more years in the case of Enterprises though it becomes increasingly expensive each year nevertheless switching is always difficult I get that and I would Not be surprised to learn that many of our listeners or their organizations were not seriously considering either paying to stay with Windows 10 on their current Hardware or perhaps switching to the arguably Superior alternative offered by zero patch it rubs me the wrong way for Microsoft to be charging its customers to fix security flaws in its own products when it is
already fixing them anyway and has a well-running system in place that allows Those fixes to continue being delivered what Microsoft is planning to do next October is to deliberately disable the existing windows up update for Windows 10 users who choose not to pay to have Microsoft continue to repair their own software flaws what's wrong with this picture as we noted last week the United States government recently opened a broad antitrust investigation into Microsoft's abuse of its Monopoly power so Microsoft Choosing to force the obsolescence of hundreds of millions of PCS or hold their customers Ransom
over fixing those software flaws in their own products could not come at a better time we've seen that it's possible for Microsoft to examine its own behavior and change when it's shown to be wrong in the case of their cloud computing security they were previously offering paid security enhancements through logging that should have been included At no charge as part of the base offering rather than being disabled by default once it became clear that this conduct was unusual and wrong they began including those additional Services free of charge October is still 10 months away and
there's time for another policy change regarding the future of Windows 10 and 11 stay tuned yeah I doubt they will we'll see it's just again it they're they're making those updates available To people who pay yeah and and they're disabling they're disabling that for Windows 11 like [Music] like just okay let's take a break so I can calm down later let's make sure that the break is not sponsored by Microsoft and then oh yeah we're good okay I don't think we've ever had Microsoft as a sponsor I don't think we ever will think that's GNA
happen at This rate ain't gonna happen they don't even sponsor Windows weekly but then again there's Paul thorat to deal with so I will tell you about something you've got to have everybody should have this is our sponsor for this segment of security Now is the think canary this is such a great idea uh you and I did a an event in Boston last pass event yep with uh the guy who created the first known Honeypot was it Steve bellan I'm trying To remember who it was or Bill Cheswick it was Bill Cheswick oh I'm
sorry yeah Cheswick Bill Cheswick uh and chz who is a great guy said it was a lot of work it was a very technically sophisticated thing to do what's a Honeypot we've talked about that on this show many times in fact on our first show it is a device on your network that looks like it's uh harmless right in fact it doesn't it doesn't even look vulnerable it looks like something valuable looks Like something a bad guy would go oh there's where the treasure lies think of it yeah it's a treasure chest that looks so
valuable on your network but inside surprise it's not a treasure chest it's an early warning system it's a Connect if you will in the coal mine that's the think Canary is but now they've solved that whole technical issue of how hard it was to do that chz was talking about they've made it simple and easy the things Canary it's a Honeypot looks About like a external USB drive has two connections one to the wall one to your network one ethernet connection you can deploy it literally in minutes you can go into the hosted console and
choose what the device looks like to the bad guy mine is a sonology Nas and I mean they do it right it's got a sonology MAC address it's got the DSM software it's got the login it's got everything I mean really looks like a genuine sonology device maybe it's an open SSH server Maybe it's a Linux box or a Windows box maybe it's um a very vulnerable Windows 95 you could make it you can make it be a skat device I mean the sky's the limit they have hundreds of different profiles so you select it
from the dropdown and you could turn on if it's a server you can turn on which services are available light it up like a Christmas tree back here or just you know some select Port 139 let's just leave that open and see what happens now here's the thing you You said it and you forget it you walk away mine's just running in the corner but here's the thing if somebody is accessing things to Canary brute forcing that fake Nas or that fake SSH server or if they're accessing the lore files because that's the other thing
thinks Canary could do you can actually create files that look like PDFs or docs or excels anything you want but if somebody tries to open it or tries to get into that server you're going to Immediately get an alert from the things Canary that says hey you got a problem you have a malicious Insider or a bad guy but somebody is probing your network and here's the thing no false alerts just the alerts that matter so it's very simple plug it in connect it to the network choose a profile for your think Canary device register
it with a hosted console it's going to the monitoring and it's going to send you the notifications by the way this was designed by people Who have been teaching companies and even governments on how to penetrate systems so it is hardened you're not putting a risky device on your network this thing is super welld designed to be really hard really really secure and not to give you a bunch of false warnings you set it up you can get alerts text messages email it supports web hooks it supports CIS log it has its own console you
could it has an API if you want to write it's kind of sky the Limit any way you want to get notified you could have your Smartwatch say hey there's somebody in your network but when that bad person that malicious Insider or the attacker makes themselves known by accessing your things to Canary or its lure files you're going to get the notification and you're going to know you got a problem on average companies don't find out for more than three months that they've been breached that's three months the bad guys get to Wander around inside
your network exfiltrating customer information User data looking for where your backups live doing all sorts of nasty stuff three months of course if You' got the than Canary they're going to go straight to that treasure chest and try to unlock it and you will know pricing let's talk about pricing most you know if you're a big bank or a casino operation backend operation you're going to have hundreds of them Small business like ours might have let's say five go to canary.is you get your own hosted console you get upgrades support maintenance and if you use
the code twit in the how did you hear about a box you're going to get 10% off the price for as long as you use things scaries oh and here's something else if you at all like skeptical get it because you can always return your things Canary you have a TW Monon 60-day money back guarantee for a full refund so there's no risk I will point out that in the seven years twit has partnered with thinks Canary no one has ever asked for a refund not once so I think they work pretty well visit canary.is
Canary and if you're interested go to canary.is box you'll save 10% for Life thanks canaries these things are genius Go to canary.is Steve Gibson okay so uh while we're on the topic of Windows or Microsoft Martin Brinkman writing for ghacks titled his piece hackers claim to have cracked Microsoft's software licensing protection almost entirely oh boy uhhuh he writes a team of hackers claim and it looks legit a team of hackers claim that they've cracked almost there's a quote almost the entire Windows sloff software licensing Protection unquote the Breakthrough allows them to activate almost any version
of Windows and office permanently windows and office installations require activation this may happen behind the scene or when users enter product keys workarounds and hacks have been available for a long time one popular choice requires running running a single line of instructions from a power cell prompt to activate windows8 or later or office the creators Of the solution claim that they found ways to extend this to even more windows and Office Products the new method works on any Windows client or server version and in includes extended security updates which Microsoft starts charging for next October
unless they change their policy and Microsoft customer specific volume license Keys CSV lks the method used up until now could not activate everything permanently but now for the first time the versions that had Remained elusive have been supported Windows 7 8 and 8.1 any recent Windows Server add-ons and extended security updates are all added the hacky says for example Ena support for Windows 10 ESU once it starts in October 2025 the hackers claim that the discovered method is simple it does not require third-party file installations or system file modifications according to a post on X
okay now I've captured their posting to X Which was posted by at massg grave Mas ssgr a in this instance the reason they chose this moniker is Mas stands for micros soft activation scripts and they posted hi at everyone they said we're thrilled to share some groundbreaking news from the at massg grave R&D team exclamation point our team has successfully cracked almost the entire Windows Office soft anyway so they just repeat basically what Martin quoted them saying for anyone who's Interested I have the x.com link to this posting in the show notes and also the
Powershell Mas scripts all right now I'm about to do this Steve should I be is it scary is it nerve-wracking should I even do this uh so I have a key I installed a second virtual machine and uh of course the product key was asso where the first one I could go back and figure it out but what if I just ran their little Powershell script here what do you Think oh it said no okay so maybe it's complaining about not uh something abouts yeah not getting a TLS Channel I'm not sure why not I'm
online all right this was probably a foolish thing anyway so I'm glad it stopped me yeah okay well right I mean it's downloading and running software from the internet oh actually it's it is uh it is a local Powershell script that that as far as I know does not need access to the Internet oh but that but this was I was using that first uh option so maybe that so anyway so so I recognize this is controversial right but this is now not any secret first of all the scripts are hosted on GitHub which Microsoft
owns um oh yeah you're right and they're they're posting on X when I looked the first time I looked it had 93,000 views wow then I looked the next day and it was 96,000 more than 96,000 so again cats out of the bag um I U I did download because I was curious I went to GitHub Microsoft's property looked at their and downloaded a zip containing their Powershell scripts they look very comprehensive they are very uh complex and detailed uh you know I didn't spend much time with it since I have no particular interest in
any of this I just wanted to report what has happened because it's news and I'm sure that many frisky Script kitties out there literally script kitties are already enjoying many hours of playing around with this to see what it does uh Martin finishes his reporting by writing an example screenshot of a fully permanently activated ated version of Windows with extended security updates has been shared at part as part of the post the methods have worked for years this is Martin writing according to one of the follow-up posts the hackers claim that The digital license work
their digital license method worked since 2018 and that the KMS method whatever that those are for at least 17 years the discovered hack will be made available in the coming months according to the original post on X so I'm I'm a little confused by that because it looks like what's there is the whole deal maybe you're right Leo maybe there is some piece of it that is that it's obtaining From the net although it looked like to me there was a lot of of of script there a Powershell script that was doing the all of
the heavy lifting he writes the discovery is a serious blow for Microsoft provided that the hack is indeed as foolproof and easy to apply as claimed it's unclear how or if Microsoft will react to the hack for now it seems that the hackers have at least temporarily won the battle I I'm not sure that I agree that It's a serious blow um you know Windows is now free essentially right I mean it's loaded down with Microsoft's crap that that you get as part of it for and and certainly they're being paid for you know the
start menu to come pre-loaded with all of this junk so there's that um also um I posted the link over the weekend Leo and we know Paul holder well he related anecdotally that his experience of reporting this to somebody I mean like Like years ago reporting this they just sort of shrugged like they know about it they don't care I think you know they figure yeah okay well we're you know we're selling bits that don't cost us anything so if some of them get stolen fine uh you know for for my part I've been a
paid up Microsoft developer Network you know msdn developer for decades you know I pay for the privilege of installing whatever Windows additions I need for software development and Testing but it is going to be interesting to see how this develops over time um you know I never I can't get it to run so okay yeah it's just uh I don't know what I'm doing wrong but well if Powershell scripts are finicky you know they it may need some other module or you may uh did you right click and run it as an admin so ah
maybe I need to do that huh there is that kind of thing too oh I bet I didn't do that yeah sure okay well so I mean I probably Shouldn't do it on on air anyway cuz then there'd be video evidence of it so well again I I don't know what the count current what what the current count is I'm going to click on the link right now we're going to find out um the current the current number of views of that posting last time I looked it was 916 plus th000 okay now we're at
918 A5 thousand views so again wow not not a secret anymore uh and you know people are Reporting that it works so w very cool and again you know again I uh I never really thought about cracking the activation system you know but it's obviously been something of a preoccupation for some segment of the hacker Community for quite a while and you know again it's it's like now you get windows with any hardware that you buy and if you set up your own Hardware I guess what you I guess you have to pay a few
hundred dollars for it Or you know ask somebody else for their key or you know who knows anyway you can buy I you could buy Keys online for pretty cheap too so yeah I I think it's anyway just of interest for and I thought I would report it because I'm I'm sure that we have some some in some parties among our listeners who will think hey this is cool I'm going to do what Leo did set up a VM and play with it see what yeah I mean the thing is I have a paid uh
license I just have to Move it over and this is easier than doing that yeah yeah okay so Apple was just granted a patent like a week or two ago with the title identity recognition utilizing face Associated body characteristics and that serves to give some sense for where and how future AI will become packaged into consumer devices because this is an AI and know an AI based patent the gist of the patent is that from the standpoint if You think about it from of a fixed security camera someone's face provides the most useful recognition detail
but the camera might not always be able to see the person's face so while the camera is seeing the person's face and is able to identify them it will also now per Apple's patent be taking note of other things the clothes they're wearing at the moment you know that day and their body dimensions and their walking gate then that person may Later be recognized not by their face which might not be visible at the moment but by association with the other available characteristic details that had been previously noted at an earlier time when their identity
could be positively determined so okay it's a roughly you know the same sort of strategy that a human Observer would employ and the fact that the US patent and trademark office granted Apple a patent on this suggests That the AI Revolution is going to further swamp the already buried USPTO as people apply for patents on a gazillion other seemingly obvious things that AI will soon be making commonplace I have a link to this in the show notes for anyone who's interested but it's like I think what the expression is Katie bar the door or something
it's like wow you're going all country on us that's great wow I mean it's like you know my This has always been my problem with patents there is a a phrase in the law that in like in patent doctrine that says that that some a so-called invention is not suitable for patent if any if anyone reasonably trained in the art would would see this if it would be obvious to anyone re reasonably obvious to anyone trained in the art meaning that okay do is this like some flash of Inspiration by a genius Apple developer or
do they have boor patent attorneys in copertino who are saying just kind of give us something like and people are saying okay how about this one and know oh that's great we'll write it up we'll get a patent you know it is abuse of the system but on the other hand that's what patents have become right you build a portfolio as a defensive measure so that you're able to do things other people are doing and when they say hey we got a Patent on that you say okay yeah but you know you're doing things that
we're doing so let's just agree not to sue each other and we'll keep everybody else frightened wow okay unbelievable I know uh Mashable caught an interesting story last week their piece was titled Zoom Li about encryption in 2020 now it wants to pay1 18 million to make that go away unquote and they tagged it with a subhead the internet never forgets though Mashable wrote back in 2020 Zoom was one of the hottest software companies in the world and of course you and I were using them Leo because uh you know I mean covid happened right
and it works it works well it's a good it works yeah um they wrote its video conferencing software surged in popularity due to millions of people being confined to home uh at in in offices home offices due to the covid-19 pandemic un fortunately the company cut some Corners When it came to the privacy of its users despite zoom's claims that its video meetings were endtoend encrypted it later came to light that this was not true the result was a class action lawsuit that Zoom settled for $85 million in 2021 Zoom also settled with the Federal
Trade Commission over misleading its users about the privacy and security of its core product but the matter did not go away entirely there's also the separate matter of a US Securities and Exchange Commission you know SEC probe into zoom's privacy policies which the SEC launched in 2020 now Bloomberg reports that Zoom is offering to settle the matter with the SEC by paying an $18 million fine the offer is still pending approval by the SEC these days Zoom does offer endtoend encryption for its video meetings and its privacy and security practices have improved but back in
2020 the company's track record was poor with zoom bombings Remember instances of people hijacking other people's Zoom calls and harassing them becoming something of a trend the Mashable article finishes by noting by the way if you've missed it Zoom is no longer called Zoom Video Communications which was its official name until Monday the company is now officially called Zoom Communications to reflect the fact that it now offers a suite of communications tools Beyond its video conferencing platform and in fact one of Them is a shared uh a cloud word competitor you know Cloud you know
shared notetaking and and document editing uh capability anyway we spent a lot of time talking uh and covering Zoom back during during those explosive days and we knew that we knew that its security was stumbling a lot during those early days I recall you know that we talked about the zoom bombings as they were known but I don't remember whether we actually knew that they were Lying about uh at the time about their video conference calls not being truly end to end encrypted it certainly it is it is challenging to do that the easy way
to do it is to encrypt to the hub you know a zoom Hub so have have each each conference link encrypted to the hub but then decrypted there for redistribution and re-encryption out to the other members of the of of the the video conference which is presumably what they were doing but that's not end To endend you know that's you know they get to decrypt and and and uh and then re-encrypt so that's probably what was going on uh and you know if if they're now doing it properly that's a good thing so one of
the problems posed by cloud services especially in this era of Big Data where big can increasingly mean really ridiculously humongously big is the question of how to seed the cloud by transferring massive amounts of data to An from a cloud provider who will after that transfer then become its host to answer that need Amazon has launched the first of their so-called AWS data transfer terminals um here's what Amazon explained on December 1st under the headline new physical AWS data transfer terminals let you upload to the cloud faster they wrote today we're announcing the general availability
of AWS data transfer terminal a secure Physical location you know like like a Kinko's print shop where you can bring your storage devices and upload data faster to the AWS Cloud the first data transfer terminals are located in Los Angeles and New York with plans to add more locations globally you can reserve a time slot to visit your nearest location and upload data rapidly and securely to any AWS public endpoints such as Amazon simple storage service you know a Amazon S3 Amazon elastic file system that's the Amazon EFS or others using a high throughput connection
and there they mean really high throughput they said using am using AWS data transfer terminal you can significantly reduce the time of inges data with high throughput connectivity uh at a location near you you can upload large data sets from fleets of vehicles they're just giving examples operating and collecting data In Metro areas for training machine learning models digital audio and video files from content creators for media processing workloads and mapping or imagery data from local government organizations for Geographic analysis after the data is uploaded to a you can use the extensive Suite of AWS
services to generate value from your data and accelerate Innovation you can also bring your AWS snowball devices to the location for upload and retain the Data for continued use and not rely on traditional shipping methods you can find the availability of a location in the AWS Management console and reserve the date and time to visit then you can visit the location make a connection between your storage device and S3 bucket initiate the transfer your data and validate that your transfer is complete uh I I got a kick out of this on your reserve date and
time visit the location and confirm access with the Building reception you will be escorted by building staff to the floor and your reserved room of the data transfer terminal location don't be surprised if there are no AWS signs in the building or room this is for security reasons to keep your work location as secret as possible and you know this sort of thing makes sense after you hear it right once these AWS terminals are available in many major metropolitan areas it's easy To imagine you know then becoming quite popular the other thing that occurred to
me when they said you know don't be surprised if there are no AWS signs in the building or or the room is this could all be time shared like all other Cloud providers you know th this could be a provision made by some entity which is creating a A multi-use high bandwidth access to the internet facility and you know the the other providers are also uh going to be Announcing similar Terminals and gee what do you know they're at the same physical location and you know it may not just be AWS that that is using
that I got the sense I saw a photo of a long Corridor with lots of doors and uh the sense that it might just sort of be a a general purpose uh access to the cloud facility so anyway kind of a cool idea uh the GRCC short cut I created to quickly take People to that pentester website which you and I both you used when we were talking about this Leo which you know it allows anyone to quickly check for their data among all of that which was leaked by the national public data breach is
the number one most clicked shortcut of all time it's grc.com [Music] yesterday one of them was reminded of this clicked the link and found that it was no longer taking them it was taking Them to pentester decom but unfortunately those guys at pentester decom were unable to resist the temptation of monetizing the traffic that was generated so the shortcut no longer takes you there uh I'm not going to take people to the site when they've you know when they've sort of done a bait and switch so just takes you to a page at GRC that
says we're sorry but uh these people uh were unable to resist the Temptation of monetizing the the traffic so anyway my point here is as I've observed since unregulated data Brokers just by their very existence just the the aggregation of what is available on the internet that aggregation itself represents a clear and present danger to Society at large so I was glad to encounter the news that the US Federal Trade Commission had taken regulatory action against two us-based data Brokers the FDC has banned mobile Walla gravy Analytics what a name and its subsidiary ventel with
two ends v n Teel from selling the geolocation data of their user that is of the data that has been aggregated the FDC cracked down on the three companies after they were caught collecting and selling the information they had aggregated without their customer's consent right it's very much the way we never gave the the the credit bureaus our explicit consent to at least You know that we knew of to be collecting our data they just you know got it the FTC said that the data contained information about military sites churches labor unions and other sensitive
locations and the FTC specifically singled out mobile Walla for selling geolocation data to identify women who visited pregnancy centers and individuals who attended George Floyd protests so it's difficult to find any sympathy for such parasitic companies um I I should also note that when I did a sort by the the frequency of clinks clicks on grc's shortcuts the second most popular GRC shortcut was GRC dopin P which are longtime listeners actually you don't have to be a longtime listener because it wasn't that long ago uh uh to took us yes to that wonderful graphic Heat
map which clearly showed the extremely nonuniform distribution in the four-digit pins chosen by those who use Pins so just a reminder that we have a lot of fun on this podcast two excellent short codes keep them both have have them ready okay I did that pentester website you may remember and was dismayed by yes you and I both found our data and significant ly Lisa's data was not because she had subscribed to a data scrubbing service y okay last week I received notification from diger that they had approved the use of Grc's Ruby G logo
for display in grc's Bey certified email I guess the internet archive came back up yep our Be Me Up Scotty podcast was back on October 15th and at the time the internet archive which the entire industry uses for this purpose to verify the long-term use of corporate logos was suffering a long running and debilitating series of Dos attacks uh you know and I'm sure that if my need was urgent enough I could have reminded diger before now and pushed the Matter but you know they did need they they did get back to it on their
own without me needing to do so so when I checked last week after receiving that notice the certificate status was in awaiting final status I'm mentioning this um because uh today I awoke yesterday to the news that grc's verified Mark certificate which was the goal of all this had been approved and was issued although I could have hosted the pair of files one's an SVG a Scalable VOR graphic and the other is a pem p uh certificate from my own grc.com domain I decided that it might seem a little more official if those files came
from dig aert themselves though I doubt that it matters either way but since they were pleased to offer to host the files I took them up on that offer so then yesterday Monday morning I added a beamy text record to GRC DNS which contained the twin URLs for grc's logo image and its matching Certificate from that moment grc's received email was be me enabled since I didn't yet have this week's email ready I sent last week's email to my Gmail account since Gmail is one of the providers that supports the display of beamy logos and
sure enough there was grc's Ruby G decorating the opened email I imagine that everyone who receives this week's email and all subsequent email from GRC through be me supporting providers will also receive The same thing whether they notice it or not and actually that's confirmed now I got a whole bunch of email from from from people and I don't know if they if they looked at the show notes and saw me talking about it or looked at this probably just the synopsis where I do mention that but a whole bunch of people wrote back and
said I see it I see it I see it so indeed although there were some people who didn't see it and that's just because their email provider isn't Yet yeah most aren't showing it do you have to turn that column on in uh Gmail or is there some no it's just there it just shows up and I did okay so I I was also curious to see whether the authentication change would have a retroactive effect so I went back a week in my Gmail to last week's originally sent email I I have my Gmail account
subscribed to this podcast uh you know to to the mailings for exactly this sort of testing interestingly the new GRC Logo was not also shown on that piece of older email which I thought was interesting since the email itself does not carry any hint of what whether the mailing domain may have a certified be logo so it appears that Google is checking for the be record at the same time as it's verifying the mailing sites SPF dkim and dmark status you know validating that and then once that's done and the email has been received the
logo is either established or it won't Ever be oh I see I see it oh that's so cool there is I just sent myself a email from is that it right here over on the left yep that's it that's really cool and what it you it used to just show that that the the silhouette of a person you know their their head and shoulders and now it's actually grc's logo nice very cool it is nice that's a that's so you don't have to insert that or anything it's just always be there from now on yep
it Come it it is BAS so it It's associated with a domain and so it is so a query to text records for or that specific text record at grc.com returns to URLs which so one the the SVG is the graphic and and then this there is a signed certificate diger signed a certificate for that graphic both of those URLs get pulled and that allows the the graphic to be affirmatively con like you know associ iated with the grc.com domain and any Email that it generates so it is neat yeah I mean I don't I
have to see if my FastMail does that but that's Gmail definitely does that's very cool yeah very cool and Leo break time and then we're GNA plow into some feedback from our listeners all right actually I've got a neat conversation about uh uh some subtleties of of third party uh or uh second Factor authentication use so oh uh a goodie good all right our show today brought to you by Speaking of uh authentication our good friends at bit Warden which is yes perfect timing perfect timing the password manager trusted by thousands of businesses and millions
of individuals like me of course uh bit Warden will let you generate and autofill strong unique logins does something else though it also autofills credit cards identities even pass Keys directly from the inline autofill menu without leaving the page that's a good thing because it won't Autofill it on a spoofed site so it's another way to protect yourself bit Warden continues to expand its integration ecosystem this is for businesses across well maybe not maybe not just businesses but if you are using enterprise software all the most important platforms you'll get seamless operations and elevated security
as an example here's some uh very popular Integrations Microsoft InTune a lot of people use that to stay secure in Business right it enhances device security and user identity management by enabling secure Bit warten app deployment on any InTune managed endpoint that includes desktops and mobile devices in other words InTune will now automatically install bit Wen if you wanted to I think that's awesome do you use ripling for HR of course ripling will also is smart about bit Wen bit warten integrates with Rippling so that it's easy to onboard and Offboard uh people it teams
can assign and revoke access to the bit Warden vault as employees join or leave do you use vanta for compliance longtime sponsor on our Network vanta compliance audit and Reporting will a this is really cool will actually add your secure password manager bit warten so that it's reported in your compliance report which means it'll be better and easier for you to meet sock 2 or ISO 271 or other standards here's the Coolest one I really want to know more about this rapid 7 is a security platform right it ensures improved threat detection or response when
it integrates with bit Warden it can correlate credential usage with security events bit Warden says oh yeah that person logged in at that time and you can correlate that to the events that that is incredible strengthening proactive monitoring and intelligence for Enterprise security Teams this is this is neat these Integrations increase flexibility let you centralized Security Management across existing technology stacks and employee devices to maintain control over sensitive information there's Integrations with many many Enterprise apps bit Warden users can seamlessly connect the tools they use for it management compliance and security to bit warten to
improve and standardize the deployment of Enterprise credential Management throughout your organization I think this is important to mention because I think sometimes when I say and sing its Praises bit I say bit warden's open source GPL open source that's really good news businesses might say well that's that rules us out right because they're not going to have all that support for Enterprise stuff they do they do your business deserves a cost effective solution that can dramatically improve its chances of staying safe Online you deserve business Warden switch today it's it's so easy B Warden setup
only takes a few minutes they support importing for most password Management Solutions and of course because it's open source bit Warden source code can be inspected by anyone but it's also regularly audited by thirdparty experts and bit warten publishes the results of those audits so you know exactly you know exactly how secure it is get started today with bit Warton's free trial of a teams or Enterprise plan but I always always want to mention that because it's open source bit warten is free for individual users and that means all devices iOS Android Mac Linux um
whatever I've left out windows I must be thinking that Windows as an individual user is free unlimited pass Keys unlimited passwords unlimited you could use your Hardware UB Keys free forever because they're open source bit Wen.com twit for your business bit warten for your yourself bit warten for your business bit wen.com SL twit oh and Steve I I I finally figured out I was misusing the instructions uh for that um unlocker and once I figured out the instructions I had to download a CMD file ah okay and run that so that was the automated thing
was to download it and it for some reason couldn't get online or whatever uh oh I know why because Edge said oh no This is not safe and I'm sure that that's also in the system oh no we're not going to let you download from uh something called Mass grave no no you're not going to download that so once I said no no it's fine I'm going to download that uh I was able to download it double click it gave me the options worked oh worked uh Paul thinks and I think he's right that actually
it emulates an Enterprise uh credentials or activation Server what it called the kwm server it it there is one that's one of the the two activation that's the loophole right oh yeah I'm an Enterprise and just connect to my server here you're okay you're good even it even said registered to Leo leport it did the whole thing so thank you I and I'm not cheating I bought a license I just wanted to move that license over yes you yes you own a license you know why cuz the original Parallels version of Windows was 22 H2
and in order to get 24 H2 I actually had to download it from Microsoft and install it and so that was not activated so now it is thank you Steve cool thank you hackers again you can imag you could see how it would be like a preoccupation right like we're gonna crack this thing you can also see how it's a really dumb thing to do what I just did which is download and run a file from the Internet but you know that's yeah that's just me you were doing you were doing it in into a
VM and you uh that's true it is in a VM yeah yeah yeah okay so Jamie uh denizard or Hae sorry haime is and he gave me his pronunciation haime uh said Steve I've been using Google Authenticator with cloud backup disabled for years but I would like to use a more featureful solution and one preferably not run by Google the main feature I'm looking for is a solution that has a web Portal so that I can get tops from any browser instead of needing my phone with me at all times how much security would I
be giving up if any if I went with a solution that offered this such as bit Warden authenticator um uh ente o or twillow ay thank you and keep up the great work hii okay so I chose ha's note because this is a question many people have I I I get it like all and we talked about it but I figured I'd just give it a little More attention and from in the future we'll just refer to this they you know they want the added security of a second Factor but they don't want the added
inconvenience we've talked about the inherent danger of merging all authentication into a single source for example of having one's password manager also supplying the one-time passcode second Factor you know is it as secure as maintaining an entirely separate second Factor authenticator and then Transcribing the six-digit code manually no is it more secure than not bothering with any second Factor yeah of course absolutely it all boils down to security models and asking the question what exactly are we wishing to protect against we need to ask that question because unfortunately there are many different points of potential
vulnerability okay so let's address three cases a full breach of the site being authenticated to a breach of only The site's known usernames and passwords or a breach of a user's computer in the first case of a full breach of the site being authenticated to the only form of Authentication that remains safe after such a full sight breach is pass Keys pass Keys remain safe because being a public key authentication system as I used to say of squirrel but I'll now say of pass Keys pass Keys gives sites no secrets to keep the only thing
a site can do with a Public key it has received from its user is verify their identity it cannot be used in any way to assert or spoof their identity one-time passcodes will not protect their users after a full sight breach because one-time passcodes rely upon a shared secret it's that secret which determines which six-digit code is correct every 30 seconds so if bad guys are able to obtain the username names the password hashes and the shared secret onetime password Seeds they'll be able to impersonate the site's users and even if the site is storing
its users passwords as salted hashes as any modern site now should a credential stuffing attack that's backed up by having each accounts matching second Factor seed would still be able to succeed so to recap in the event of a full sight breach traditional second Factor authentication which relies upon the continued secrecy of a shared secret seed key would provide no added Protection so it would not matter whether your own authenticator is storing its secret separately or for example in your browser okay in the second case of only a breach of a site's usernames and and
has passwords or even without any breach just guessing usernames which are increasingly email addresses the bad guys would employ as I mentioned before a so-called credential stuffing attack that's the new fancy name you know which We used to call Brute Force attacks although credential stuffing suggests that the stuffer is not just guessing randomly but is instead working from a list of known possible credentials that have been previously harvested from some other service and this is where reusing passwords between sites becomes a very bad idea however in this case since the bad guys would not have
obtained any of the sites stored second Factor Authentication Secrets the use of a second Factor authenticator would strongly protect the user's account and again where the authenticator is running whether it's in the user's browser or offline in a separate smartphone would make no difference since the bad guys would have no way of guessing the continually changing six-digit passcode okay so to recap that in both of the previous two instances of a tax a full sight data breach or one of the Increasingly common credential stuffing attacks the location of the users authenticator has no impact and
makes no difference this brings us to the third case a breach at the user's end this could either be a breach of the user's PC with their web browser and its password manager or a breach of the user's smartphone which contains their second Factor authentication Secrets if that's what they're using this is the nightmare scenario where the only Protection is the separation that hopefully exists between the first and second authentication Secrets the presumption is that it's exceedingly difficult for any bad guys to get into either of the users authentication stores the first or the second
factors because we never see that happen right we're constantly talking about all manner of Horrors on the internet and with internet related Technologies But we never encounter instances where users are having their local password managers breached if I had some wood handy somewhere I would knock on it since we don't ever want to be reporting that well there is the exception of the last pass breach well okay but that wasn't a local breach of the that that that you know that was headquarters being breached right okay yeah yeah so it's so it's not the ACT
you know we you know we don't see we're not ever reporting stories of like some problem with some password manager that turns out has a horrible problem right and so this this substantiates our intuitive sense that it's safe except for robo form which was used to hack people's wallets right so it was that was Generator had a bad random RNG so yeah yeah um so but your point is valid absolutely right uh the the but so the The point is all the evidence we have um not only theoretically but but practically is that we're not
seeing problems with password managers being able to keep their secrets they are and given that it's exceedingly difficult to break into one credential store it's beyond exceedingly difficult to imagine that two separate credential stores using wildly differing Technologies a PC and a smartphone might both be simultaneously compromised in order for Bad guys to obtain both first and second Factor secrets and then facilitate spoofing authentication okay in other words the only danger posed by by storing both the first and second authentication Factor secrets in the same place in the same device and thus under the same
form of protection is that the security of that device could possibly conceivably be breached and moreover we're aware of no instances where that has happened or has been a Problem so the the the the two the MFA is not stored in a vault the secret is stored in the Vault on last pass's servers though or or bit warden's servers actually copies are downloaded to to your local browser the yeah but I'm just saying if they were if those sites if if as would happened with last P if the Vault has been exfiltrated H that I
mean that's a good point if they secret is in that Vault if if they're holding the both first and second and Headquarters is breached then then like all their users are Up theek This is highly theoretical right and as we've said before you know you're probably fine doing yes I have a separate app just for that reason that's all and and I actually I I wrote in the show notes so at this point today it's only a theoretical concern and argument right but it is but it is nevertheless a concern and an argument no matter
how theoretical it may be which you know We've just brought up right it could happen and something did happen at last pass so you know this is very much like our recent discussions of whether it's safe to leave an otherwise unprotected wire guard VPN service port exposed and listening on the internet you know as tens if not hundreds of thousands of people do as I said last week it's very much almost certainly safe there's every reason to believe that it is safe and no reason to believe that it isn't right up Until the moment that
we learn that it wasn't right so you I'm spending so much time on all this because it's an important concept that binds these together the concept is layered security the idea of layered security is that no single fault vulnerability or compromise in the security of something protecting a system would result in a compromise of that system security another more colloquial term for layered security would be belt and Suspenders I would always put wire guard I would behind some other form of Access Control if only so that any failure of either one would not result in
a failure of the whole and the concept of layered security is what gave us multiactor authentication in the first place not relying upon any single Factor if one is compromised the other can be trusted to hold ideally the implementation of layered security doesn't pose an ongoing burden upon its User and this is where the implementation of the system comes into play If The Machine a a user is authenticating from already contains a reasonably fresh previous authentication cookie depending upon the security you know needs of the website it would be reasonable to bypass the request for
the user's second factor and only ask for it if either a long time has passed since the user last authenticated from that machine or the user is authenticating From a machine that has no record of previous authentication this model continues you know the model of doing that only prompting for second Factor when there's some some reason to do so um you know you know still strongly protects the user from an online credential stuffing attacker for example whose authentication guesses would not carry the second Factor bypass cookie While also reducing the annoyance factor to repeat users
of the same machine so haime your question was obviously a good one because it certainly didn't have a short answer and the answer that it did have is best viewed in the context of the various possible threats that it needs to protect against practically speaking I think a good case could be made for most users to just let their existing password managers painlessly Supply their second Factor one-time Passcodes for them that provides strong protection against the known online password stuffing style attacks that we know are occurring and against those attacks it is providing layered belt
and suspenders authentication protection the fact that it is not also protecting from a theoretical attack that we have no evidence of ever having happened you know not being a problem uh even though the protection could be provided by moving those second Factor secrets to a Different device is almost certainly taking caution too far until it isn't I keep my second Factor tokens in my smartphone my browser doesn't have them they're not online they except in the sense that they are they are synchronized through iCloud and stored encrypted for the sake of synchronizing and I appreciate
that although I really don't have to do that either because I add them so infrequently and I always Print out the QR code if I need to synchronize devices or you know to to to restore well there's your weakest link if somebody breaks into your house he's got the QR codes now you're really in trouble there are not any Russians or suspicious looking foreigners lurking around I think that's really the other side of that equation is how much harder is it to store it in a separate a program I don't consider that a big jump
in difficulty so I do it yes haime Is saying his bar is lower right he you know he it bugs him having a and maybe he's using some sites that are not well-designed and so they're constantly asking him when he's sitting at the same nonshared PC it's like I just gave this to you yesterday that would be annoying yes yeah yeah I mean most of us have have static IPS so so the site could could could encrypt our IP into the cookie so that it can see if the ey you Know I mean there's all
these things that could be done where you know like properly to to properly use a second factor and it's unfortunate when sites don't you know bother more and more I'm seeing sites force me to reauthenticate a lot yes uh and it's really annoying yes but I guess we live in a dangerous world uh Nur Eden said dear Steve I've been a dedicated listener of for of security Now for many years your show has Expanded my technical understanding and reinforced important values I deeply believe in particularly that privacy is a fundamental condition for Freedom accountability to
the entire internet community and unwavering reliability regarding remote access Solutions while overlay networks like wire guard and nebula work well they lack granular ACC access control and could be complex to set up Solutions like cloudflare tunnel and enro provide Public facing interfaces but I needed something different I wanted to create a private tunnel from my home Raspberry Pi SSH server to my laptop so I could log in from anywhere I wanted to connect a cloud web server to a micros service that runs on another Cloud I wanted to link database servers and clients running on
different locations he says I developed a solution based on SSH tunneling through an external server since both ends make all Outgoing connections opening ports or modifying firewall settings is unnecessary I have developed a simple web interface so connecting two devices is as simple as setting up a zoom meeting meaning clicking on a link after using it successfully for years to connect public Serv connect cloud services and and remote control devices I've made it publicly available at www.pet pc.com P PP tpc.com he says it is currently free to Use as I want to see how far
this solution can go thank you ner Eden I went over to www.pet pc.com and took a look around the site looks very clean and new and I imagine it will evolve over time there is not yet any deep technical documentation that I could see so I know that many of our listeners would need to know why they should trust it but I'm aware that others won't care that much and may just be content to play with Whatever it is so I'm not vouching for it in any way since I cannot but I wanted to share
this very Nic looking creation of one of our listeners to give Nur some attention to his efforts that might be ful to him and to reiterate how amazed I am by the quality of the people who choose to spend their time listening to this podcast so thank you for the share uh ner www.pet pc.com Steven uh sedron wrote hi Steve I heard you mention tour's call for more Bridge operators in SN uh 103 last last week he said I wanted to bring to your attention the snowflake extension SL add-on for Firefox Chrome Brave or other
chrome-based browsers it allows the tour network to use your computer as a proxy to help people circumvent censorship and it's as easy as installing a web browser extension SL Add-on you can also toggle the settings to allow it to continue running even when the browser is not open they're good about not slowing down your internet connection and they hide your IP address while someone is connected through your computer the snowflake also changes from purple to green in color if pinned to the toolbar at the top so you know when someone is currently connected he said
I want to mention this to you and hopes people might help the tour Network in this way as well because not everyone has the skill to run a server to run a bridge as I do not the easiest to set up in Linux he notes he says read more about it here and then he gives the URL uh snowflake. torproject.org okay so that is very cool I love that something like this could be so easy to set up and be safe to use the tour project folks certainly know what they're doing and just to Explain
these this snowflake this proxy uh serves as a middleman in between uh nodes to the the tour servers do all of the fronting of connections but as we know it's very useful to bounce traffic around a while within the tour Network in order to increase its security so that's the so you're not an end node nobody SE SE your IP address you're one of the internal nodes that just gets used to to scramble the traffic up that's how um T is able To keep from overloading your your bandwidth um one of the reasons I'm very
glad Stephen put this on our radar is that these days most of us have massive bandwidth Overkill you know with our bandwidth mostly sitting idle so the idea that we might be able to donate some small piece of our bandwidth to help the tour project and to provide some more diffusion seems like a great idea I followed Steven's link and went over to the tour projects snowflakes Page it turns out that snowflakes function as a traffic proxy is only one of the things it's able to do it also allows the users who install it to
use the the tour system so they said snowflake is a system that allows people for from all over the world to access censored websites and applications similar to how vpns assist users in getting around internet censorship snowflake helps you avoid being noticed by internet sensors by making your Internet activity appear as though you're using the internet for a regular video or voice call there are numerous tools available such as snowflake that transform internet activity each using a different technique some redirect internet and and they mean numerous tour tools he said some redirect internet traffic to
appear to be coming from popular Cloud providers like Microsoft Azure and Amazon web services others scramble internet traffic in order to Make it appear completely random it therefore becomes costly for sensors to consider blocking such circumvention tools since it would require blocking large parts of the internet in order to achieve the initial targeted goal unlike vpns you do not need to install a separate application to connect to a snowflake proxy and bypass censorship it's usually a circum it it is usually a circumvention feature embedded within existing apps currently snowflake is Available inside tour browser on
desktop and Android Onion Browser on iOS and Orbot on Android and iOS if you've downloaded and installed any of these apps and they are censored in your country you can bypass the censorship by activating snowflake through the app settings page and then we get to the part that caused Steven to write his note the tour project writes did you know that snowflake proxies are operated entirely by Volunteers in other words a Tour user gets matched with a random snowflake volunteer proxy which is run by a volunteer like you so if you want to help people
bypass censorship consider installing and running a snowflake proxy the only prerequisite is that the internet in your country is not heavily censored already you can join thousands of volunteers from around the world who have a snowflake proxy installed and running there's no need to worry about which websites people are Accessing through your snowflake proxy their visible browsing IP address will match their tour exit node not yours there are various different ways to run a snowflake proxy begin or to Advanced he and then it said install the web extension the web extension is the easiest way
to run a snowflake proxy simply install it on Firefox Chrome or Edge enable the extension and watch the icon turn green when a user connects through your proxy yeah so I've Installed it on my browser and it's up in this upper right hand corner it's very small it's purple right now but that's cool I'll know when somebody's using it it'll turn green oh that's neat and you're just you have become part of the tour Network while you choose to have your your browser open or even if you select an option it it'll you'll allow it
to keep running even if your browser's closed but as long as your as your computer is on obviously and it Allows you to you know to be part of the of of the mixing of traffic that the tour system is is providing I especially nowadays yeah I think we need it very cool y so thank and thank you for bringing the snowflake to our attention Stephen John Robinette has a solution for linking smartphones and PCs he said hey Steve with regard to your wish for a way to easily type something on your PC and send
it to your iPhone I would recommend local send and referred To local send.org he said the simplest way to describe it is a crossplatform airdrop written in Dart plus flutter that works on iPhone Android Linux Windows and Mac it does require installing an app but the communication is all local between devices local send uses mdns to discover other local send clients on your subnet which then allows you to send and receive text files photos and so on he says I've been using It for about a year to move files various files between my Windows PC
iPhone iPad and a Linux PC so very crossplatform he says if you don't want to install an app there's also paop at pdr.net which is similarly uh which is similar but entirely browser-based the actual transfer of data is peer-to-peer via web RTC however establishing this peer-to-peer connection depends on both clients first making a connection to the Website so it won't work if your internet connection is down or if you're paranoid about using someone else's server but it's open source and easily selfhosted if you're that person hope that one of those or both of those might
be use useful for you or others so and of course nowadays on a Mac anyway you have this iPhone access so you can use this on your Mac right and on PCS you have it for uh for Android devices actually you can sort of use it with IPhones as well so and apparently that is the casee and I actually we're about to get to that oh okay sorry so I like I like these two apps though that's really yes they are very and very very cross-platform yeah so um uh J sock said good afternoon Mr
Gibson he's being formal long time sock please to meet you and he says long time first time you got me into bug Bounty and I now make a insignificant amount of income through through bug Bounty interesting huh yeah He said my wife is obsessed with oh this is this is the soda stream guy my wife is obsessed with lacroy and we've spent a lot of money on it over the years he says this year I'm thinking about getting her so a soda stream like device it is the season so she can get her fix more
easily and we can hopefully save some money I remember that you discussed some techniqu techniques you had used to save some money on a similar device on the podcast and I'm going to go through The notes and find that information what I would like to know is if you have any updates to your previous process as I recall you had changed the adapter on the CO2 cartridge and we're getting your CO2 canisters refilled somewhere in Irvine he said I'm in Fullerton do you still do this has this process held up over many uses and years
would love any thoughts you have on whether this is a worthwhile investment or not thanks for sharing your very valuable time okay I'll take up just a bit of everyone's valuable time because it has been such a win for us the trick is to have a single large CO2 Master tank that's used to directly refill empty Soda Stream canister little mini tanks that the soda stream uses this allows you to perform the refilling from the big tank to the little tank at home using the soda stream canisters over and over again and really part of
it was saving money it was just annoying to have to like pain To ship those back continually recycle the the these canisters yes and the master tank can in turn be re be be filled over and over by any home home brewing shop now I was I tried this and I was unable to find anybody who was willing to do that so oh okay you may you may have lucked out there in Irvine yeah I've got one off of Bristol a few like a mile away and so people so you do want to verify that
first right and you may want to get the tank from them Because that was one of the issues is a lot of people said well I'm not going to fill some strange tank they they they wanted to know it was something that they had imagine the the tank from them is probably no more expensive right um although it does have to be a special tank so first of all people who Brew their own beer at home use the you know the same tanks and get them refilled okay the one the first trick is interconnecting the
two tanks and Amazon Has plenty of adapters for exactly this purpose they are typically nicely machined brass adapters that have a valve one end of the adapter fits the empty Soda Stream canisters and the other end mates with a standard CO2 tank which is also available from Amazon I believe mine is a 20 lb tank I bought one and then and then pmed it off on mic and he didn't want it CU we couldn't get it filled so I think we gave it away I wish I had known I would have sent it to Our
to our correspond yeah definitely make sure you're able to fill it they're about $150 so they're not inexpensive but it's the the 20 lb one was light enough for me to drag and roll from my car to the shop for refilling and back the only requirement for the tank is that you need to be sure to get one with a so-called siphon tube the siphon tube extends from the valve on the top all the way down to the bottom and that's What allows you to fill the empty sod stream canisters with liquid carbon dioxide taken
from the bottom of the tank rather than CO2 gas which will be taken from the top um and as I said they're not inexpensive they're about $150 but uh it's been worth it for us and I have not counted the number of times we're able to refill a small canister from the much larger tank but it's many many many times I I mean I Know I think I've only gone to the the home brewing place maybe three times in total and they had no refilling the tank but if but but you might you know certainly
it makes sense to buy it from them as long as they can provide you with one with a siphon tube because you do need to have that for sure otherwise you have to turn the thing upside down while you're doing it that's no fun you don't want to do that okay finally Troy in Montana Suggests Intel's Unison but then there was one other he said Steve longtime listener since day one if if you have an Intel PC well we know I have those you can use their app to connect your iPhone to a PC and
get access to sending messages not perfect but a way to do what you hoped and then he provides a link to it's intel.com and it's their something that they call Unison he says thanks for all you and Leo do to keep us safe so okay I was excited when I read Intel's description it says following a simple pairing process between the phone and the PC you can make or take phone calls from your PC send or receive text messages using the PC's mouse and keyboard and view phone notifications on the PC screen also you can
seamlessly and bidirectionally share photos videos and documents between your phone and PC the Intel Unison solution fully supports both Android and iOS and and I mean like they I have a I put A picture of what they have on their website in the show notes it looks like a like a fullsize desktop version of iMessage on the screen with all the contacts and and messages shown I mean it looks utterly amazing but when I drilled down a bit more I tripped over the following quote the Intel Unison application is available for download on any Windows
11 PC that meets the minimum requirements as detailed in the App Store Descriptions both laptops and desktops are supported so for anyone who has already made the move what was it that that mic the the M the Microsoft guy said who had transitioned to Windows 11 yeah yes that's right uh this it really looks like more than I could have ever dreamed of uh you could actually have apparently a functioning messages app sitting on your Windows desktop uh with your phone nearby on its charger um I already have A need to run a Windows 11
VM since the work on the DNS Benchmark which is what I'm doing now has turned up some subtle but important differences in Windows 11 handling of some app resizing so I was planning to get Windows 11 set up under virtual box in any event but if I could load this onto that machine I might have Windows 11 VM running 247 so thank you for that Troy and then Hinrich Johnson said unfortunately not available for Windows 7 but supported in Windows 10 And later he said you can check out phone link should be built into windows
and enabled by default and and there's a link uh then the show notes uh and the the URL ends with sync across your devices and he says and Heinrich says you can read and answer text see any notifications and even make phone calls from your computer it uses Bluetooth underneath to make the magic work he says I just switched from Android and really was really missing Push bullet but this is pretty this is a pretty solid replacement okay so it appears it appears that my prayers may have been answered and that the frustration I've been
feeling has not been mine alone and that solutions to this have been created I don't know how or whether this is related to Intel's Unison but it looks like the same thing and Intel is just sort of private labeling the the same uh you know W Windows application I I was a bit nervous cuz I I tracked down phone link and there Microsoft says requires Windows 11 but Hinrich clearly said Windows 10 so I'm hopeful Microsoft might just be refusing to in any way promote the continued use of Windows 10 so like they've just scrubbed
it from their website so anyway uh thank you Hinrich and also thanks to all of our listeners who heed my call and my please for a solution and Leo yes after this break let's chat let's talk about GPT all right and by the way I I've been using phone link for some time on uh Windows 11 I know I'm not sure if it works on Windows 10 but I bet it does uh it works best with Android but you see we can send text messages I'm connected right now to an Android device my my my
Z flip my Samsung Z flip and it really does work Beth with Samsung you know but I've been able to use it with iPhone it just doesn't have all of the features I don't need all I just need my sanity Preserved so well I can't promise you that Steve you know that but that may be a that yeah that may be a yeah all right before we get back to the uh matter at hand which is of course everything exciting and wonderful that Steve is talking about I thought it might be a good idea to
take a little break and remind you about the most important thing you're going to do today which is join Club twit now many of you are already members of Club twit uh and for Those I am very grateful because they've allowed us to continue on the air you might have noticed though fewer ads on this episode uh all of our episodes M Breck wickley had no ads for some reason I think some uncertainty about the economic future I don't know uh advertisers have really disappeared right now at this point in podcasting it's the top 10
podcast to get half all literally half of all the advertising and the rest of us are left begging for Scraps and the scraps just aren't there I always thought it'd be fun to make this network be a listener supported back in the day when you and I started Steve there just weren't any really good infrastructure ways to do that we do have them now thanks to patreon and we use a patreon company called memberful we can uh we can do that and it's still my hope that we could maybe make this entire network supported by
you our listeners you know what we could do it All we would need is about 5% of the audience that's all to join the club we wouldn't have to put stuff behind pay walls we could expand we could add shows we could add content uh but until we get 5% joining ain't G to happen right now it's uh somewhere less than 2% one isn't that sad one in 50 people who listen to this show are subscribers let's let's up that I by the end of the year I want to get 5,000 new subscribers we almost
have to get 5,000 new subscribers to survive Into 2025 help us out now there are benefits it's only seven bucks a month ad free versions of this show and every show you wouldn't even hear this pitch for Club twit uh it is it is uh there there are other benefits I mean there there's the club twit Discord which is a great place to hang out and chat about everything Geeks are interested in that's where our Advent of code uh group hangs out there's also um you know special events and shows that we put on The
club we did an advent of code last week I did live live coding crazy huh uh for the first I think four days of Advent of code that was a lot of fun Stacy's book club is coming up on the 19th uh also Mike's crafting Corner he's doing little a little tiny a little tiny kitchen or something little tiny rooms but you don't have to do that you can do whatever things you're interested in it's just kind of a cozy hang there's also Chris markarts a photo review Coming up on Thursday I can go on
and on we do a lot of great stuff in the club we give you video for shows that are Audio Only in public things like that uh but the main reason to do it is if you appreciate this show and all the shows we do and you want them to keep going we need your support twit.tv Club twit all right let's get back to security now uh okay so I'm G to warn our listeners that the introduction here Is uh dense but it is important it is not actually important to understand every Nuance of what
I'm going to explain although some people will find it interesting so so for them uh and because this is what happened I want to you know in order to set in order to set this up for the conversation that I have it's important okay so as I mentioned at the top I had an interesting interaction with the coding version of chat GPT 40 which they call uh 40 with canvas and That's while I was working on the update that I'm working on to grc's DNS Benchmark um and as as I've been me as I've mentioned
recently I've been using the coding platform version uh as sort of a super Google search on steroids I'm often astonished by the quality of its replies something that I don't understand happened over the weekend while I was working on code but frankly I don't understand any of this AI stuff it's all Voodoo and that's the problem Because I'm 100% certain that this is too important for us to not understand and I have a plan for that but let me first share what happened okay one of the facilities of Microsoft's macro assembler which I use to
make my assembly code more con prise that is one of the features that I use uh and more legible is the assemblers macro facility I have a macro named it happens to be named aend Rich edit which it takes a string argument that is the macro takes A string argument so in my program code I would write for example append Rich edit and then in quotes a benchmark results now the way Assembly Language macros work is that when the source code is being assembled the assembler does what's called macro expansion which causes it to follow
the simple macro script to create additional code from that script the point is that this is all nicely hidden behind the macro which just says aend Rich edit and Then a string in quotes which makes for a more readable program in the case of my append Rich edit macro which as I said takes a string argument when the code is being assembled the macroscript places that string argument into the program's data section then it writes a call to my append Rich edit function passing it a pointer to that string I could have done the same
thing by hand but this creates a much clearer communication and one thing I've learned From yes 55 years of programming is that coding is all about communication I almost as much about communicating to me as it is to the computer which is why my code is frankly it's beautiful I mean it's it's I you know it's it it the computer doesn't need it I've seen people write Assembly Language where there's a bunch of of op codes down the leftand margin of the page and it's like what is this crap mine you know it's about communication
Okay so the use of this macro simulates the semantics which everyone is used to in highlevel languages where it's possible to use a literal string as an argument in a function call you know th this would be like writing in the basic programming language you know you you you would write print quote hi Mom exclamation point close quote you know it's very convenient but in Assembly Language the string hom needs to be defined elsewhere in a data section of The program and then the address of that string is provided to the print function for it
to print so this is very efficient if you might have some repeated use of the string hom throughout the program since all of those repeated instances can all reference that single high mom data string but the need to define the string elsewhere in the program that is from where you're using it makes the resulting code somewhat less clear by Default Assembly Language doesn't offer the highlevel language convenience of in place string declaration and use so I use a macro to give me the same semantic flexibility essentially it looks like a higher level language is being
used although it's still lowlevel underneath okay so I apologize for the long and esoteric you know inside baseball explanation but I wanted to explain the situation surrounding what I was about to ask chat Gp4 about what I needed was the ability to optionally add a another argument to the macro if that optional argument was present it would be provided to the function call which the macro wrote for me and if I did not supply that optional argument to the macro the macro would provide a default argument in its place now this is not a feature
of masm masm is Microsoft's macro assembler masm That I frequently use but I knew that masm allows the specification of both required and optional parameters what I wasn't sure about was having it Supply default values for non-specified parameters but since masm has a very powerful macro facility thus called a macro a Microsoft Macro assembler I had the sense that it probably had the capability to supply a default value for missing optional macro parameters To get the details of something like this once upon a time back in the old days which in this case is about
two months ago before I started using chat GPT for these things I would have Googled around a bit to see whether I could quickly find an answer but more often than not since the sorts of things I'm looking for tend to be somewhat obscure I would wind up reading a couple of pages of the masm documentation but now we have chat GPT Which as I've mentioned I've been using more and more so the first thing I do now is ask it so I got a chat GPT prompt and I wrote quote can I use a
macro in masm where an optional macro parameter has a default value if it's not specified question mark close close quotes I mean that that's that's that's exactly the phrase I put in to which chat GPT 40 quickly replied yes in masm and it helpfully Added Pen's Microsoft Macro assembler you can create a macro with optional parameters that have default values if they are not specified this is achieved by using the ifb directive to check if a parameter is blank and it says pen I.E not provided Clos penss and then assigning it a default value within
the macro here is an example to demonstrate how to define and use such a macro colon and then it gave me some sample code okay Now right off the bat the syntax it showed for the macro seemed suspicious the way it was specifying a default value looked wrong to me it it was a construction that various higher level languages use but I thought well I did ask so I modified my original macro definition as chat GPT had specified and masm was not at all pleased with it since chat GPT seemed quite clear and authoritative in
its answer I first made sure I hadn't made some mistake but Everything looked good I tried tweaking it myself and doing some various things sort of variations on that theme but nothing I tried worked so I replied to chat GPT and this may be the first time I've ever done this I wrote that didn't work the syntax of the first line of the macro definition was incorrect any ideas and chat GPT replied you're you're right mm's macro syntax you're right I'm an Idiot it's like yeah it said you're right yeah Mac mm's macro syntax doesn't
directly allow you to specify default values in line in the macro definition and then it quoted its own previous incorrect sample code with with with an example he said and and and for example it the quote is param 2 equals and then a default value in angle brackets you know in in in uh less than greater than uh symbols then it said it said period then it said However you can achieve the same effect using the ifb directive to test for blank parameters and handle them Ma and handle them manually here's a corrected example colon
and then it gave that and although I needed to modify what it provided for my needs that second attempt worked okay so to recap I asked this thing which often conversationally refers to itself in the first person which is still a little Annoying and Jarring it's an it not a you know it doesn't have pronouns um so I asked this thing a question it quickly provided an authoritative sounding and reasonable answer which was nevertheless wrong then I pointed out that you know the part of the answer that was wrong and it said you're right and
then proceeded to offer a corrected answer but I remained haunted by my original impression that masm did in Fact allow default values to be specified for optional and missing parameters you know this kind of the way my my mind works I mean I still remember all of the word star keystrokes because they were you know built into me into they've got some deep neurons in my brain because I used them so you know so much so I went to the source which is where I would have wound up in the old days and the masm
reference revealed the truth it is indeed possible to specify a Default parameter for an optional and unspecified macro paramet chat GPT was almost correct the first time it simply forgot that a colon and an equal sign were needed to separate the parameter and its default value instead of just an equal sign so it gave me an answer that was initially wrong but was almost right when I told it that there was a problem with that answer it agreed saying you're right mm's macro syntax doesn't directly Allow you to specify default values in line in the
macro definition which that statement later turned out to be wrong and it gave me what was effectively a workaround for the feature that it then assumed was missing from masm finally having found the correct answer to this I decided to let it know so I replied following up on this it turns out that your I'm saying your I okay It's I I don't know what else how else to address it following up on this it turns out that your first response was almost correct the proper Syntax for the first line of the macro definition is
my macro space macro space Pam 1 comma Pam 2 colon equals and then the default value in the angle brackets I said the thing that was missing was that colon in front of the equal sign okay and I hit enter and the damn thing responded ah you're absolutely correct thank you For pointing that out in masm the Syntax for specifying a default value for a parameter does indeed require the colon equals operator not just equals here's how it should look and it provided a correct example then it provided me a little tutorial with the heading
why colon equals Works writing it said it wrote to me the colon in Colon equals is required to differentiate default values from other constructs in masm without the colon Masm doesn't interpret the equal sign as part of the default value definition thanks for catching that Nuance exclamation point it makes the macro much more concise and straightforward than relying on ifb and then it actually gave me a smiley face okay I got bad news for you though Steve unfortunately it's not going to remember that so if you ask it again it's going to still make the
same Mistake un do to can you imagine the garbage that that the internet would be filling remember it locally uh because it does remember some stuff locally but you can't teach it because obviously if you could the world the end of the world as we know it it was very polite about the correction that is a very useful prompt tip that a lot of people uh have noted is you can say no that's wrong and it will actually come back to you and often Get it right so it's very interesting no I'm not dead yet
something like that I wanted to share this conversational event because I'm still startled it's amazing by this thing and because and you heard that what it apparently said about that our picture of the week that was just like amazing yeah you know and because I was left staring at the screen wondering what have we created the fact that I really have no idea Is unnerving and I know I'm not alone in being unnerved by this whatever this is as I said several weeks ago I believe it's the biggest and most significant transformative event of our
lifetimes aliens have not landed in our backyard we have created them you know it's funny you should say that because I had uh have a friend who works in the business and he said that's a better way To think of it as an alien intelligence it's just different from ours yeah yeah and it seems clear that this is just the tip of the iceberg now I have a picture at the end of the show notes Leo I have spent my entire life This Is Amazing by the way I love this picture working to understand the
way things work and I have proof of that the last page of the show notes has a photo my dad took of me at age four four at the picnic table in our backyard in orenda California wow I Needed to understand exactly how electricity worked and why you couldn't just hook up one wire to a light bulb oh because why not right the electricity comes out of the battery and goes to the light bulb right nothing has changed since then did your dad make you that board no no you made the whole thing yeah I
mean you can see the way you can see the way the kite string is wrapped around the dry cell battery a little little Excessively hey it's not going anywhere so wow I wanted to understand this uh I want you know nothing has changed since you know me at age four back then today I want to understand this whatever this is um so two days ago I identified and purchased quite lengthy Technical and detailed textbooks on the subject of large language models conversational and generative AI I am blessedly and finally nearing the end of part one
of Peter Hamilton's Seemingly endless two-part Archimedes engine novel series Once I'm finished with that I'm going to turn my attention to educating myself about a Ai and not just for myself I have every intention and expectation that I'm going to reprise my role as security now's explainer and chief to explain to this podcast audience exactly what I've learned about what we are creating ah I need to know and I'm pretty certain that among this Audience I'm not alone you are not alone so stay tuned can't wait Mr explainer and chief yeah it's a fascinating subject
um it it's just mindboggling Leo I have no idea I understand how all this other stuff works this it's I I just don't have a clue well to some degree it's Black Box I mean you can understand how it's trained and you can understand roughly how it works there's a very uh I recommend for a shorter version of these Longer books uh Steven Wolfram has done a really excellent explainer of how they work um at at one would expect he's done a lot of writing now about AI he's very interested but uh the problem is
the rules they generate are not visible and are essentially a black box and so that's kind of an interest I see you looking it up right now that's great um yeah I didn't want I I didn't want to lose that um we certainly know that's the case with neural networks right you Know they adjust their strengths based on on being trained right and and adjusting their outputs to to match what is told they should be but we don't actually understand the waiting of the neural network it's just what it does and it works Transformers are
basically a form of neural network so it's very similar uh I will be very interested to see what you've can figure out that's I can't wait well I I intend to do a a a security Now style uh Explanation of this once I understand it myself so we'll see what we'll see what we get I don't know what's going to happen Steve Gibson aren't we glad we've got him you are a national international treasure Mr G uh he is here for you every Tuesday that's when we do the show right after Mac break weekly 2
p.m Pacific 5:00 p.m. Eastern 2100 sorry 2200 UTC you can watch live on eight different platforms including uh Discord for our club twit Members YouTube twitch LinkedIn Facebook Tik Tock x.com and kogi kogi no kick uh those are the eight different platforms but most people don't try to watch live or if they do they still want a copy of the show and actually there's a few different copies you might want to get if you go to Steve's website he has the 64 kilobit audio version that's the same as we do at our website but he
also has a 16 kilobit audio version at grc.com so if you want something a little Scratchier but a lot smaller what quarter the size you can get it there but also very handy the transcripts that uh Elaine Ferris uses those 16 kilobit versions to make that really is helpful uh to read as you're listening or to use for a search engine all of that's at grc.com while you're there pick up a copy of spin right Steve didn't talk about it today but you said you had a big announcement I I thought that might be a
some sort of announcement but maybe Not um maybe I misunderstood anyway no I think I think I was just this was the I'm going to learn Ai and then share what I know I want a Steve Gibson AI so I can an ask questions of it that would be useful maybe you'll work on that too um grc.com get a copy of spinrite world's best mass storage maintenance performance enhancer and Recovery utility really is a great tool for anybody with mass storage current Version 6.1 just came out that's at grc.com lots of free stuff there as
well and of course the show if you want to get the little Ruby G in your email you'll need to sign up at grc.com mail now you don't have to get those newsletters although that's where the Ruby G will be is on the on the unless Steve personally emails you if that happens even better but uh the the Ruby G goes on those newsletters that he sends out but when you do uh validate Your email at that site what you will also get is the ability to email questions thoughts at pictures of the week security
now grc.com can't do that unless you unless you validate your EMA first yep it bounce right back at you um and he has two newsletters one is it what is the show notes by the way I didn't even mention that's another thing you can download from his website the show notes are really basically everything he talks about the show so It's very easy way to see what's going on uh we also have copies at our website twit.tv slsn there's a link there to the YouTube channel great way to share Clips that's my recommended way to
S you know you hear something on the show you know you want to say hey Steve talked about this send a clip it promotes the show helps us a lot makes it very easy for your correspondent to see what Steve said uh that's from the YouTube channel we also Of course are a podcast so you can always subscribe audio and video versions available in your favorite podcast client I think I've mentioned it everything join the club t.tv club twit thank you Steve uh good luck with and the uh engine the Andromeda engine jez God I
I'm I looked this morning I was at 89% I thought okay God 10 10% more I think I and I understand John rereading it immediately because so much happens and it's so complex that You feel like who is this what do they do what what what and so I actually opened a Apple notes and started writing stuff down so I could keep track I'm putting it I put it aside briefly because Stacy's book club is coming up on the 19th and we're doing uh James sa Corey's uh newest one he's the guy who did the
expanse and I know you're a big fan of his expanse or I should say their expanse because it's two people write writing uh his their new one um the Mercy of the Gods is really really good and I know I think you will find it very similar to Peter F actually one of my oh yeah no no I guess I'm thinking of something different I was thinking of uh Jack Campbell also has a new series uh he did The Lost Fleet series one of our and that's just it you know I I actually cannot recommend
this Peter Hamilton novel too long it is it's too much work it's it's um you know it's it Just doesn't measure up to his earlier stuff you know Fallen dragon and the the the Pandora star and Judas Unchained stuff those were just they were really good but his later stuff it's just wow are you being paid by the page well I'm really liking the new James sa Corey so I'll just throw plug for mercy of the Gods it's really good we're going to do it in Stacy's book club on the 19th so I had to
I have to finish it before the book club so I had To put Peter side sorry Peter um thank you Steve Gibson have a wonderful week with we will see you on the 17th for 1005 ooh I love it security Now [Music]